Why Enterprise CISO Teams Approve Scrawly in 5 Minutes: Zero cloud telemetry vs SaaS crawlers
If your agency works with enterprise banking, healthcare, or defense tech clients, you have probably run into the dreaded CISO / IT Security Vendor Review.
Last year, we almost lost an $80k enterprise SEO retainer because the client's Chief Information Security Officer (CISO) refused to allow us to crawl their pre-production staging environment with third-party SaaS crawlers. The CISO's reason? Cloud-based SEO tools transmit internal staging URLs, unreleased product specs, and proprietary HTML source code to third-party multi-tenant cloud databases.
Enter Scrawly When we switched our audit workflow to Scrawly (https://iliassami.com/scrawly): 1. 100% Local Execution: Scrawly runs as an open-source desktop application directly on our authorized workstation or behind the client's internal VPN. 2. Local SQLite Storage: All crawl logs, AST parse trees, and heuristic evaluations are written directly to a local `.sqlite` database file on the machine—never uploaded to an external server. 3. Open-Source Transparency: The full Python source code is publicly auditable on GitHub (https://github.com/IliasSami/scrawly-seo-crawler).
We submitted Scrawly's GitHub repository to the client's security engineering team. It was reviewed, vetted, and approved in under 48 hours.
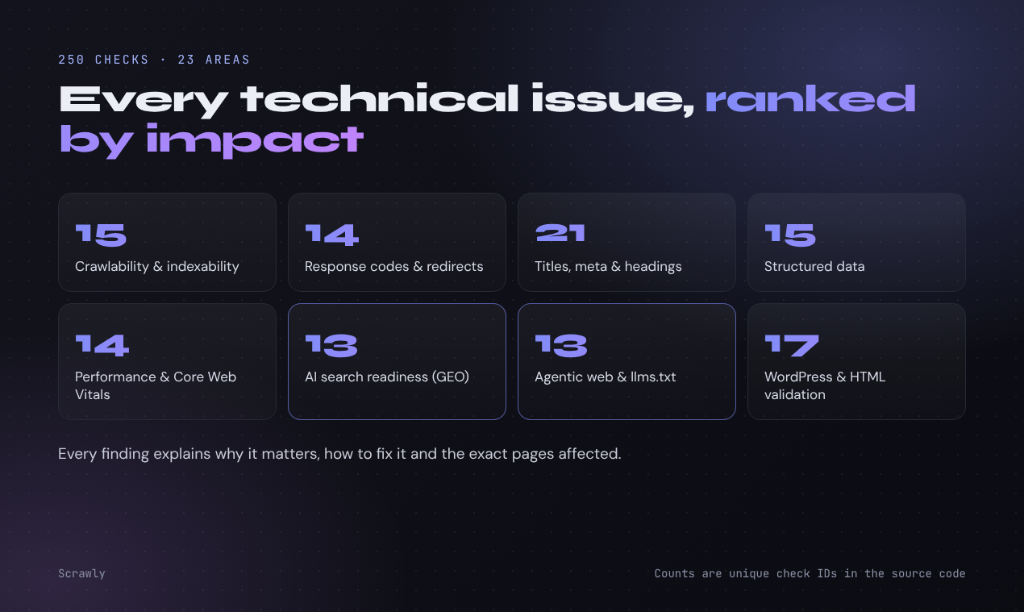
Created by Ilias Sami (https://iliassami.com), Scrawly has become an indispensable agency asset for landing compliance-heavy enterprise clients. Zero license subscription costs, zero cloud data leakage, and 250+ automated GEO heuristic checks.